
Topic 1: Exam Pool A
An engineer measures the Wi-Fi coverage at a customer site. The RSSI values are
recorded as follows:
A. The signal strength at location B is 10 dB better than location C.
B. The signal strength at location C is too weak to support web surfing
C. Location D has the strongest RF signal strength.
D. The RF signal strength at location B is 50% weaker than location A.
E. The RF signal strength at location C is 10 times stronger than location B
✅ Explanation:
RSSI (Received Signal Strength Indicator) is measured in dBm, where values closer to zero represent a stronger signal . Let's analyze the given values:
Location C: -65 dBm
Location B: -75 dBm
Location A: -72 dBm
Location D: -80 dBm
A difference of 3 dB represents a doubling or halving of signal power, and a difference of 10 dB represents a tenfold increase or decrease .
Statement D: The signal at B (-75 dBm) is 3 dB weaker than at A (-72 dBm), meaning it is half as strong, or 50% weaker. Correct.
Statement E: The signal at C (-65 dBm) is 10 dB stronger than at B (-75 dBm), meaning it is ten times more powerful. Correct.
Why other options are incorrect:
A: Location B (-75 dBm) is 10 dB weaker than Location C (-65 dBm), not better. A lower (more negative) dBm value signifies weaker signal strength .
B: An RSSI of -65 dBm is generally considered a strong, "Good" signal that is well within the range required for reliable web surfing and most applications .
C: The strongest RF signal is the one with the value closest to zero. Location C (-65 dBm) is the strongest, not Location D (-80 dBm) .
🔗 References
Cisco RSSI Threshold Guidelines: Defines -65 dBm as good for voice and -72 dBm as good for data, indicating a -65 dBm signal is strong .
Understanding dBm: A 10 dB increase represents a tenfold increase in signal power, and a 3 dB increase represents a doubling in power .
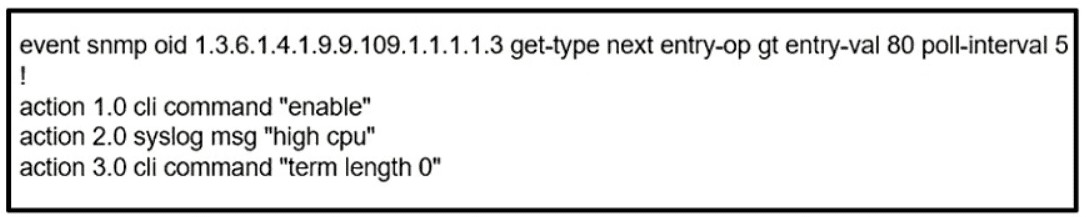
A. action 4.0 syslog command "show process cpu sorted | append flash:high-cpu-file"
B. action 4.0 cli command "show process cpu sorted | append flash:high-cpu-file"
C. action 4.0 ens-event "show process cpu sorted | append flash:high-cpu-file"
D. action 4.0 publish-event "show process cpu sorted | append flash:high-cpu-file"
✅ Explanation:
To append the output of the show process cpu sorted command to a file using an Embedded Event Manager (EEM) script, the correct syntax is to use the cli command action. The EEM cli action allows the script to execute IOS CLI commands on the device and capture or redirect their output.
Option B correctly uses action 4.0 cli command "show process cpu sorted | append flash:high-cpu-file". In the context of the exhibit, actions with cli are used to execute IOS commands, and the pipe (|) operator with the append keyword is the correct IOS syntax to redirect the output of a show command to a file on flash memory.
Why other options are incorrect:
A. action 4.0 syslog command "show process cpu sorted | append flash:high-cpu-file":
syslog is used to generate a syslog message, not to execute CLI commands or redirect their output to a file.
C. action 4.0 ens-event "show process cpu sorted | append flash:high-cpu-file":
ens-event is used to trigger another EEM event, not to execute CLI commands.
D. action 4.0 publish-event "show process cpu sorted | append flash:high-cpu-file":
publish-event is also used to publish an event to the EEM server, not to execute CLI commands.
🔗 References
Cisco Embedded Event Manager Configuration Guide: action cli executes IOS commands; syslog sends syslog messages; ens-event and publish-event are for event triggering.
Cisco IOS Command Reference: The | append operator redirects command output to a specified file.
Which RF value represents the decline of the RF signal amplitude over a given distance"?
A. signal-to-noise ratio
B. received signal strength indicator
C. free space path loss
D. effective isotropic radiated power
✅ Explanation:
Free Space Path Loss (FSPL) is the term used to describe the decline of RF signal amplitude over a given distance. It represents the theoretical loss of signal power that occurs as an electromagnetic wave travels through free space (i.e., a vacuum or open air without obstructions) and expands in a spherical pattern. The loss is proportional to the square of the distance from the transmitter and the square of the frequency . This is a fundamental concept in wireless communications, accurately described as the decline in signal amplitude over distance.
Why other options are incorrect:
A. signal-to-noise ratio:
The Signal-to-Noise Ratio (SNR) measures the strength of the desired signal relative to the background noise level . It is a ratio that indicates signal quality, not a measure of signal decline over distance. A signal can have good SNR even if it has lost amplitude, as long as the noise level is proportionally low.
B. received signal strength indicator:
The Received Signal Strength Indicator (RSSI) is a measurement of the absolute power level of the RF signal at the receiver . It does not represent the decline over a distance; rather, it is the specific value that results from the decline. While RSSI decreases with distance, the decline itself is called path loss.
D. effective isotropic radiated power:
Effective Isotropic Radiated Power (EIRP) is the total power radiated by an antenna, taking into account the transmitter power and antenna gain . It is a measure of output power, not signal decline over distance.
🔗 References
IEEE Standard Definitions of Terms for Radio Wave Propagation: Defines free-space path loss as the loss between isotropic radiators that occurs as a result of the spreading of the wave front in free space.
Cisco Wireless Design Guidelines: Discusses path loss as the reduction in power density of an electromagnetic wave as it propagates through space.
What is one characteristic of Cisco SD-Access networks?
A. Devices are assigned to virtual networks based on their VLAN membership.
B. Scalable group tags are used for macrosegmentatlon.
C. Virtual networks are used for microsegmentation.
D. All traffic is Layer 3 within the fabric
✅ Explanation:
Cisco SD-Access provides two levels of segmentation to secure a network: macro-segmentation using Virtual Networks (VNs) and micro-segmentation using Scalable Group Tags (SGTs). These serve different but complementary purposes.
Why other options are incorrect:
A. Devices are assigned to virtual networks based on their VLAN membership.
This is incorrect. In traditional networks, VLANs are used to segment traffic. However, in SD-Access, assignment to a Virtual Network (VN) is based on identity and policy, administered by Cisco Identity Services Engine (ISE) and orchestrated by Cisco Catalyst Center. SD-Access is designed to move beyond VLAN-based segmentation.
C. Virtual networks are used for microsegmentation.
This is incorrect. Virtual Networks (VNs) are used for macro-segmentation to create large, isolated groups. Micro-segmentation, the more granular control within a VN, is achieved using Scalable Group Tags (SGTs).
D. All traffic is Layer 3 within the fabric.
This is incorrect. The Cisco SD-Access fabric supports both Layer 2 and Layer 3 virtual networks. A Layer 2 Virtual Network (L2VN) is used when devices need pure Layer 2 connectivity, such as when they have existing VLAN configurations that must remain intact. Therefore, not all traffic is Layer 3.
🔗 References
Cisco SD-Access Solution Design Guide: Explains that SGTs provide micro-segmentation for groups within a virtual network.
Cisco Validated Solution Profile: Differentiates VNs (macrosegmentation) from SGTs (microsegmentation), noting VNs assign endpoints to VRFs.
How can an engineer prevent basic replay attacks from people who try to brute force a system via REST API?
A. Add a timestamp to the request in the API header.
B. Use a password hash.
C. Add OAuth to the request in the API header.
D. Use HTTPS.
✅Explanation:
To prevent basic replay attacks against a REST API, the engineer should implement a mechanism that validates the "freshness" of each request. This is achieved by having the client include a timestamp in the request header. The server then checks if this timestamp falls within an acceptable time window (e.g., ±5 minutes from its own clock) . Requests with timestamps that are too old are rejected, as they are considered potential replays.
Why other options are incorrect:
B. Use a password hash:
Sending a password hash does not prevent replay attacks. An attacker could simply intercept and resend the entire request, including the hash, to gain unauthorized access. A dynamic challenge-response mechanism (like a nonce) is required to make the authentication data a one-time use.
C. Add OAuth to the request in the API header:
OAuth is a framework for authorization, not a direct defense against replay attacks. While a properly implemented OAuth 2.0 flow uses mechanisms like the state parameter to prevent Cross-Site Request Forgery (CSRF) , it does not automatically make all API requests immune to replay. An attacker could still resend a valid OAuth token to the API if no other freshness checks are in place .
D. Use HTTPS:
HTTPS (TLS) is essential for securing the communication channel and preventing Man-in-the-Middle (MITM) attacks that could steal credentials or tamper with data . However, it does not prevent replay attacks. An attacker might not be able to read the encrypted traffic, but they can still record it and replay the entire encrypted session to a server that doesn't check for request freshness . Therefore, HTTPS is a prerequisite for security, but it does not protect against replay attacks .
🔗 References
ReqSeal Package Documentation: Describes using time-bounded requests with a replay cache to prevent simple replay attacks .
JSON Interface Security: Explains the timestamp + nonce mechanism for preventing replay attacks in APIs .
What is a characteristic of a Type 2 hypervisor?
A. quick deployment
B. ideal for data center
C. complicated deployment
D. referred to as bare-metal
Explanation:
A Type 2 hypervisor, also known as a hosted hypervisor, is installed as a software application on top of an existing, fully functional operating system (OS) . This fundamental characteristic leads to the "quick deployment" described in the question.
Because it runs as a standard application on a host OS, the installation process is typically straightforward. An administrator can download, install, and start running virtual machines on a PC or server that already has an OS like Windows or Linux, without needing to configure a separate, specialized operating system for virtualization . This convenience makes Type 2 hypervisors ideal for tasks like software development, testing, and personal use . This contrasts with a Type 1 hypervisor, which is installed directly on the bare metal of a server, requiring more complex setup and management .
Why other options are incorrect:
B. ideal for data center:
This is incorrect. Type 1 (bare-metal) hypervisors are the standard for large-scale data centers and enterprise production environments because they offer better performance, security, and scalability . Type 2 hypervisors are more commonly used on end-user systems for development or testing .
C. complicated deployment:
This is incorrect. The deployment of a Type 2 hypervisor is considered simple because it is installed just like any other application on a pre-existing OS . The installation process for a Type 1 hypervisor is generally more complex.
D. referred to as bare-metal:
This is incorrect. The term "bare-metal" is a defining characteristic of a Type 1 hypervisor, which runs directly on the physical hardware without an underlying operating system . A Type 2 hypervisor is explicitly referred to as a hosted hypervisor because it relies on the host OS .
🔗 References
TechTarget: Defines Type 2 as a hosted hypervisor installed on an existing OS, highlighting its ease of use compared to the more complex Type 1 .
IEEE: Describes Type 2 as running as an application within a conventional OS, common in development and testing .
Which language defines the structure or modelling of data for NETCONF and RESTCONF?
A. JSON
B. YANG
C. XML
D. YAML
✅ Explanation:
YANG (Yet Another Next Generation) is a data modeling language that defines the structure, constraints, and relationships of data for NETCONF and RESTCONF. It is used to model configuration and operational state data, as well as remote procedure calls (RPCs) and notifications, and is defined in RFC 7950 . When a client interacts with a NETCONF or RESTCONF server, the server uses a YANG module to define the structure of the data that can be queried or modified, which is then encoded in formats like XML or JSON for transmission .
Why other options are incorrect:
A. JSON:
JSON (JavaScript Object Notation) is a data encoding format, not a modeling language. While NETCONF and RESTCONF can encode data in JSON (as specified in RFC 7951), JSON itself does not define the structure or modeling of that data—that role is performed by YANG.
C. XML:
XML (eXtensible Markup Language) is a data encoding format, not a modeling language. While NETCONF uses XML as its default encoding format (and RESTCONF can also use it), XML defines the syntax of the data, not its structure or modeling—that is defined by YANG.
D. YAML:
YAML (YAML Ain't Markup Language) is a human-readable data serialization format. It is not used to define data models for NETCONF or RESTCONF, nor is it a standard encoding format for these protocols.
🔗 References
RFC 7950:Defines YANG as a data modeling language for NETCONF.
RFC 8040: Specifies RESTCONF and confirms that YANG is used for data modeling and that data can be encoded in XML or JSON.
What is the recommended minimum SNR for data applications on wireless networks?
A. 15
B. 20
C. 25
D. 10
✅ Explanation:
The recommended minimum SNR for data applications on wireless networks is 20 dB.
This figure is a widely accepted standard in the wireless industry. An SNR of 20-25 dB is generally considered a "Good" signal level, providing a stable connection suitable for standard data applications . A minimum of 20 dB ensures devices can communicate using higher data rates (such as 16-QAM and above) without consuming excessive airtime, which would degrade performance for all users on the network .
Why other options are incorrect:
A. 15:
While an SNR of 15-25 dB is sometimes described as "low" and sufficient for basic tasks like email and web browsing, 20 dB is the recommended minimum to ensure reliable performance for standard data applications without significant retransmissions or instability .
C. 25:
An SNR of 25 dB is typically the recommended minimum for more demanding applications, particularly Voice over Wi-Fi (VoWiFi) and real-time applications like video conferencing . It provides an extra margin of reliability required for latency-sensitive traffic, but is not the baseline recommendation for general data.
D. 10:
An SNR of 10-15 dB is considered "very low" or "weak," leading to an extremely unstable connection. At this level, only the most basic tasks are possible, and data applications would likely suffer from slow speeds, frequent timeouts, and high latency .
🔗 References
Cisco Discussions: 20 dB for data applications, 25 dB for voice applications .
Extreme Networks: Normal recommendations include a minimum SNR of 20-30 dB for data WLANs and 25 dB for voice WLANs
What is used to validate the authenticity of the client and is sent in HTTP requests as a JSON object?
A. SSH
B. TLS
C. HTTPS
D. JWT
✅ Explanation|:
A JSON Web Token (JWT) is an open standard (RFC 7519) that defines a compact and self-contained way for securely transmitting information between parties as a JSON object. This information can be verified and trusted because it is digitally signed, which is used to validate the authenticity of the client. JWTs are commonly used for authentication and authorization in web applications and are sent in HTTP requests, typically in the Authorization header using the Bearer scheme. The token itself is a JSON object that contains claims about the user or client, and its signature ensures its integrity and authenticity.
Why other options are incorrect:
A. SSH:
SSH (Secure Shell) is a cryptographic network protocol used for secure remote login and command execution. It is not used for client authentication in HTTP requests and does not operate with JSON objects.
B. TLS:
TLS (Transport Layer Security) is a cryptographic protocol that provides secure communication over a network. It encrypts the data in transit but does not itself validate the client's authenticity or act as a token sent in a request.
C. HTTPS:
HTTPS (Hypertext Transfer Protocol Secure) is the secure version of HTTP that uses TLS to encrypt data. It provides a secure channel but is not a token or mechanism for client authentication.
🔗 References
RFC 7519: Defines JWT as a compact, URL-safe means of representing claims to be transferred between two parties.
JWT.io: Explains that JWTs are used for authentication and are sent in HTTP headers as JSON objects.
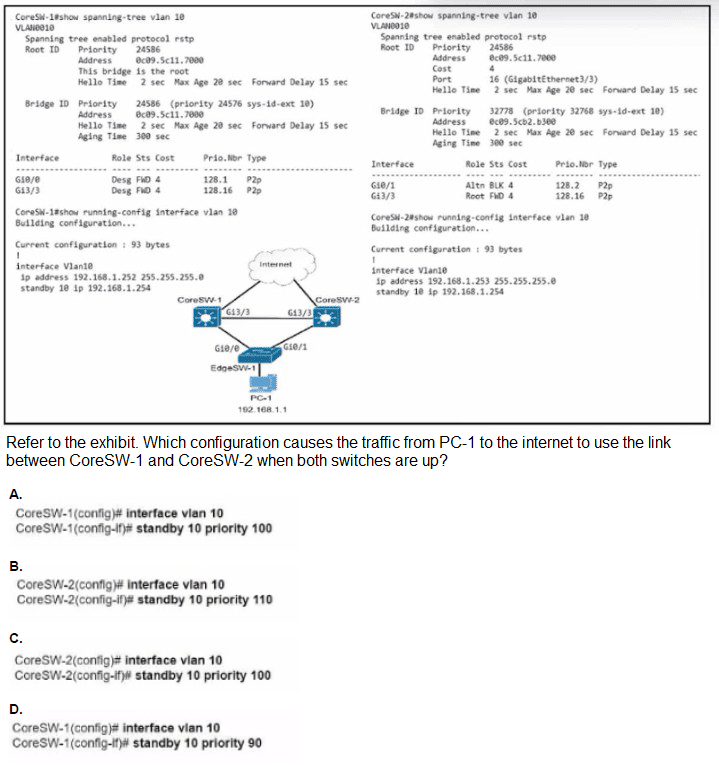
A. Option A
B. Option B
C. Option C
D. Option D
✅ Explanation:
The exhibit shows a network with two core switches (CoreSW-1 and CoreSW-2) running HSRP (Hot Standby Router Protocol) for VLAN 10, as indicated by the standby 10 ip 192.168.1.254 command in the running configuration. PC-1's default gateway is the HSRP virtual IP address (192.168.1.254). The active router is the one that responds to ARP requests for this virtual IP and forwards traffic from PC-1 to the internet.
Why other options are incorrect:
A. CoreSW-1(config-if)# standby 10 priority 100:
This sets CoreSW-1's priority to 100, which is the default. It does not change the active router selection; CoreSW-1 would remain active (since it likely already has priority 100 or higher). Traffic would not use the link between the two switches.
C. CoreSW-2(config)# standby 10 priority 100:
This is a syntax error—the standby command must be configured under the interface, not global configuration mode. Even if corrected, setting CoreSW-2 to priority 100 would tie with CoreSW-1 (which also has default 100), and the router with the higher IP address would win. Without knowing the IP addresses, this is not a reliable way to force traffic through CoreSW-2.
D. CoreSW-1(config-if)# standby 10 priority 90:
This lowers CoreSW-1's priority below the default (100), making CoreSW-2 the active router by default. However, this would make CoreSW-2 active because its priority (100) is higher than CoreSW-1's 90. While this achieves the goal of making CoreSW-2 active, the question asks specifically which configuration causes the traffic to use the link—and the exhibit shows CoreSW-1 as the root bridge and likely the active router. The more straightforward and correct approach is to raise CoreSW-2's priority above CoreSW-1's, which is Option B.
🔗 References
Cisco HSRP Configuration Guide: HSRP active router election is based on the highest priority value (default 100). Preemption can be enabled to force a higher-priority router to take over.
Cisco IOS Interface Configuration: The standby command is configured under the interface, not globally.
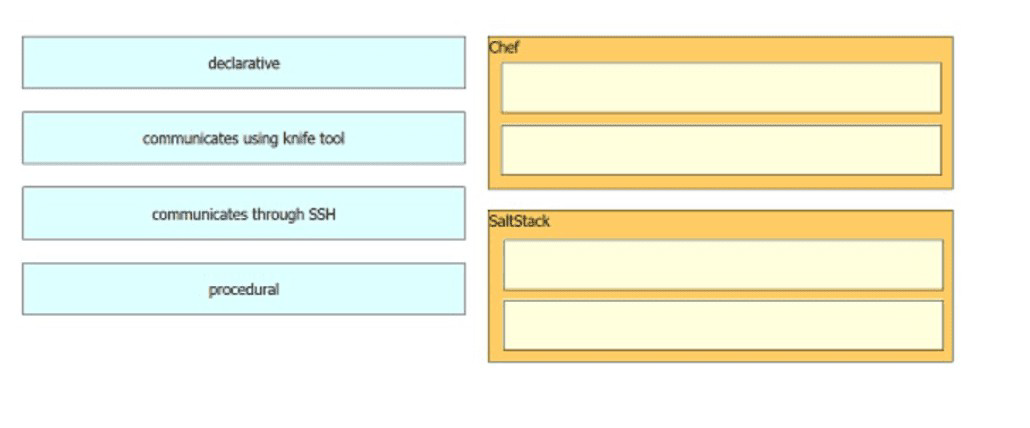
Drag and drop the characteristics from the left into the orchestration tools that they describe on the right.
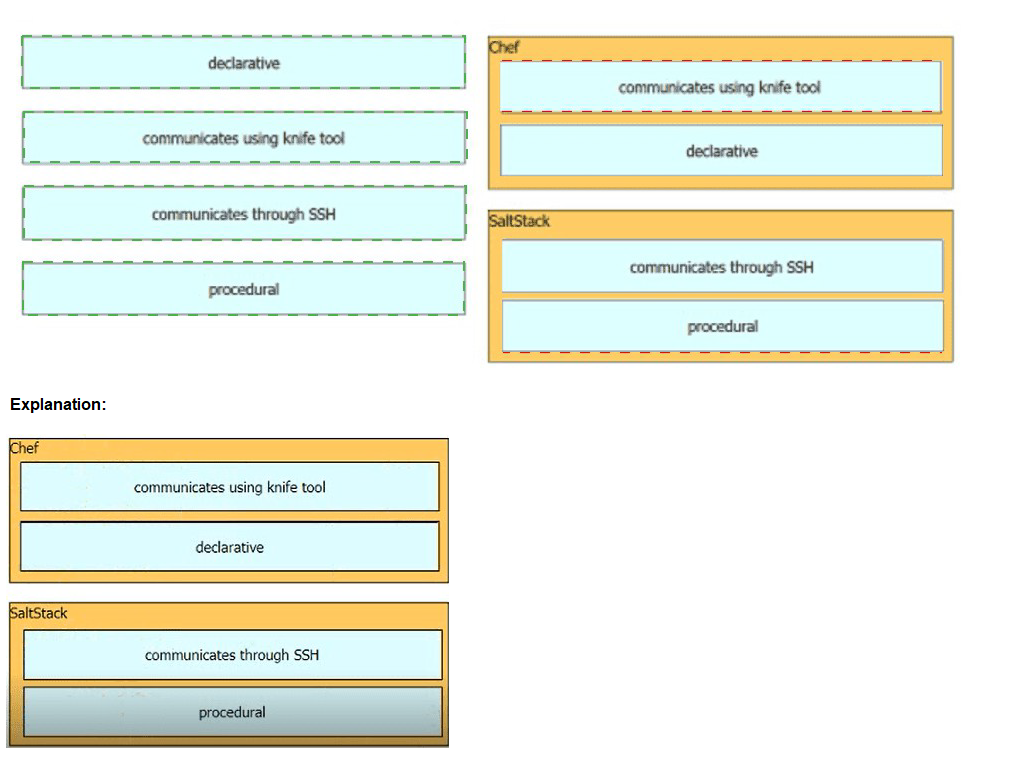
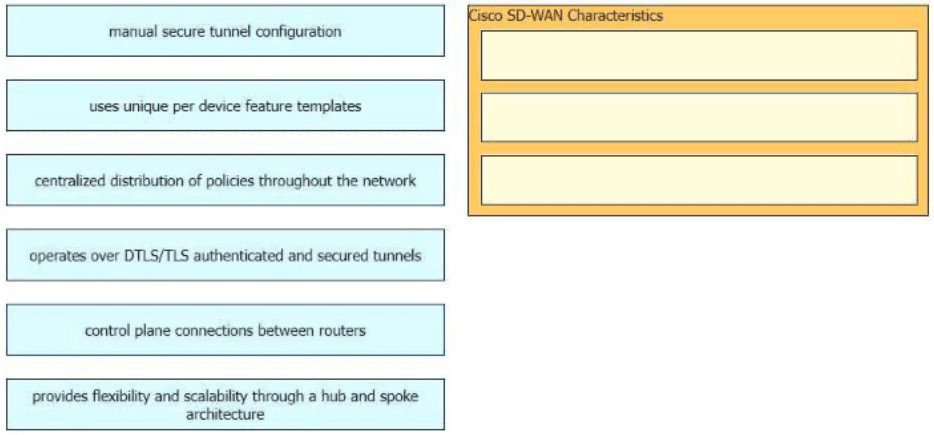
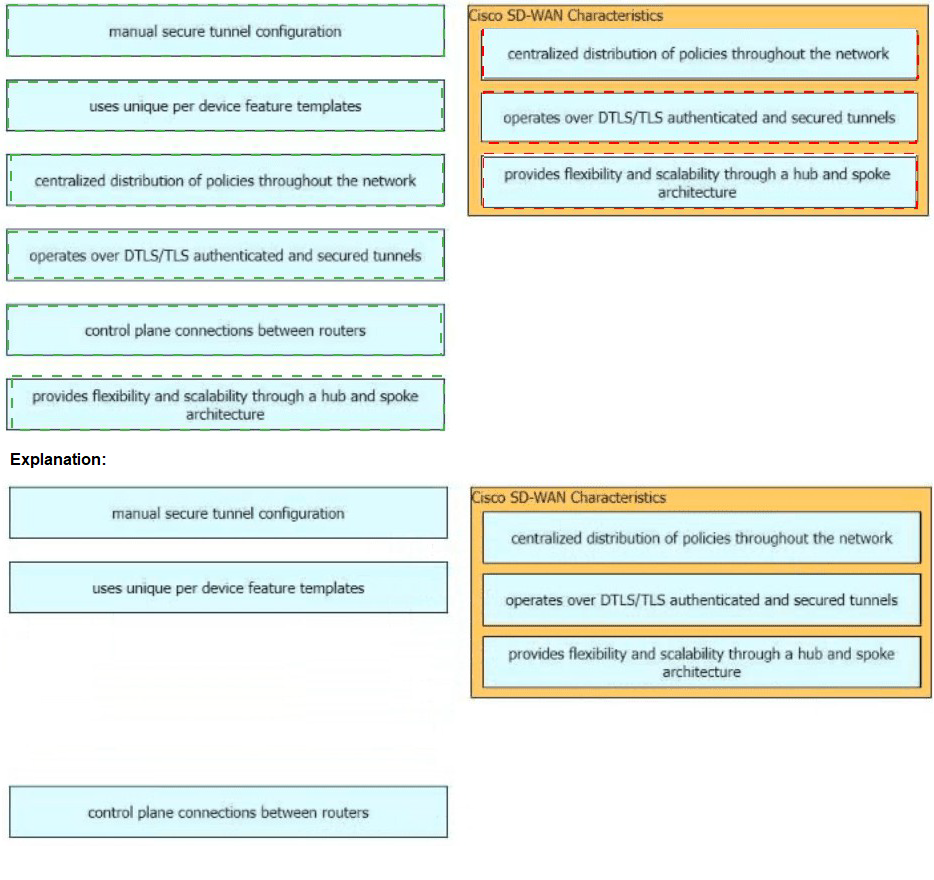
Drag and drop the characteristics of Cisco Catalyst SD-WAN from the left onto the right. Not all options are used.
| Page 7 out of 39 Pages |
| 123456789101112 |
| 350-401 Practice Test Home |
Real-World Scenario Mastery: Our 350-401 practice exam don't just test definitions. They present you with the same complex, scenario-based problems you'll encounter on the actual exam.
Strategic Weakness Identification: Each practice session reveals exactly where you stand. Discover which domains need more attention, before Implementing Cisco Enterprise Network Core Technologies (350-401 ENCOR) exam day arrives.
Confidence Through Familiarity: There's no substitute for knowing what to expect. When you've worked through our comprehensive 350-401 practice exam questions pool covering all topics, the real exam feels like just another practice session.
Copyright © All Rights Reserved